

Top 5 Anomaly-Based Intrusion Detection Systems in Canada, 2026
Anomaly-Based Intrusion Detection Systems (IDS) are sophisticated tools designed to identify deviations from established norms in network behavior and traffic patterns. As businesses in Canada increasingly prioritize cybersecurity, the appeal of anomaly-based systems has grown immensely due to their ability to detect unknown threats effectively. Unlike traditional signature-based systems, which rely on known attack signatures, anomaly-based IDS analyze data patterns to uncover potential security breaches that may not have been previously recognized. This innovative approach appeals to organizations looking for advanced protection against evolving cyber threats, ensuring the integrity and safety of their sensitive information.
Inception's AI took the time to understand this market in Canada · We may earn a commission on purchases. It never affects our rankings.
Top Picks Summary
Darktrace Immune System
Darktrace Immune System leverages advanced artificial intelligence to detect and respond to cyber threats in real-time. Its unique self-learning technology mimics the human immune system, identifying anomalies and potential risks within the network. This proactive approach sets it apart from traditional cybersecurity solutions that often react only after an attack has been detected. With its autonomous response capabilities, Darktrace provides organizations with a powerful tool to mitigate risks and maintain operational integrity.

Cisco Stealthwatch
Cisco Stealthwatch harnesses advanced analytics to provide comprehensive visibility and security across network traffic. What distinguishes it is its ability to analyze user behavior and detect unusual patterns, effectively identifying threats that may go unnoticed by conventional security tools. Its seamless integration with Cisco's broader security portfolio enhances situational awareness and response capabilities. Ideal for both small businesses and large enterprises, it offers scalable solutions for robust network security.

Where to buy Cisco Stealthwatch in Canada: the trusted retailers we track in this market, with the best price we have observed at each. Prices are checked regularly and can change, and the retailer confirms the final price at checkout.
We may earn a commission on purchases. It never affects our rankings.
$3,000 – $5,000
Vectra Cognito
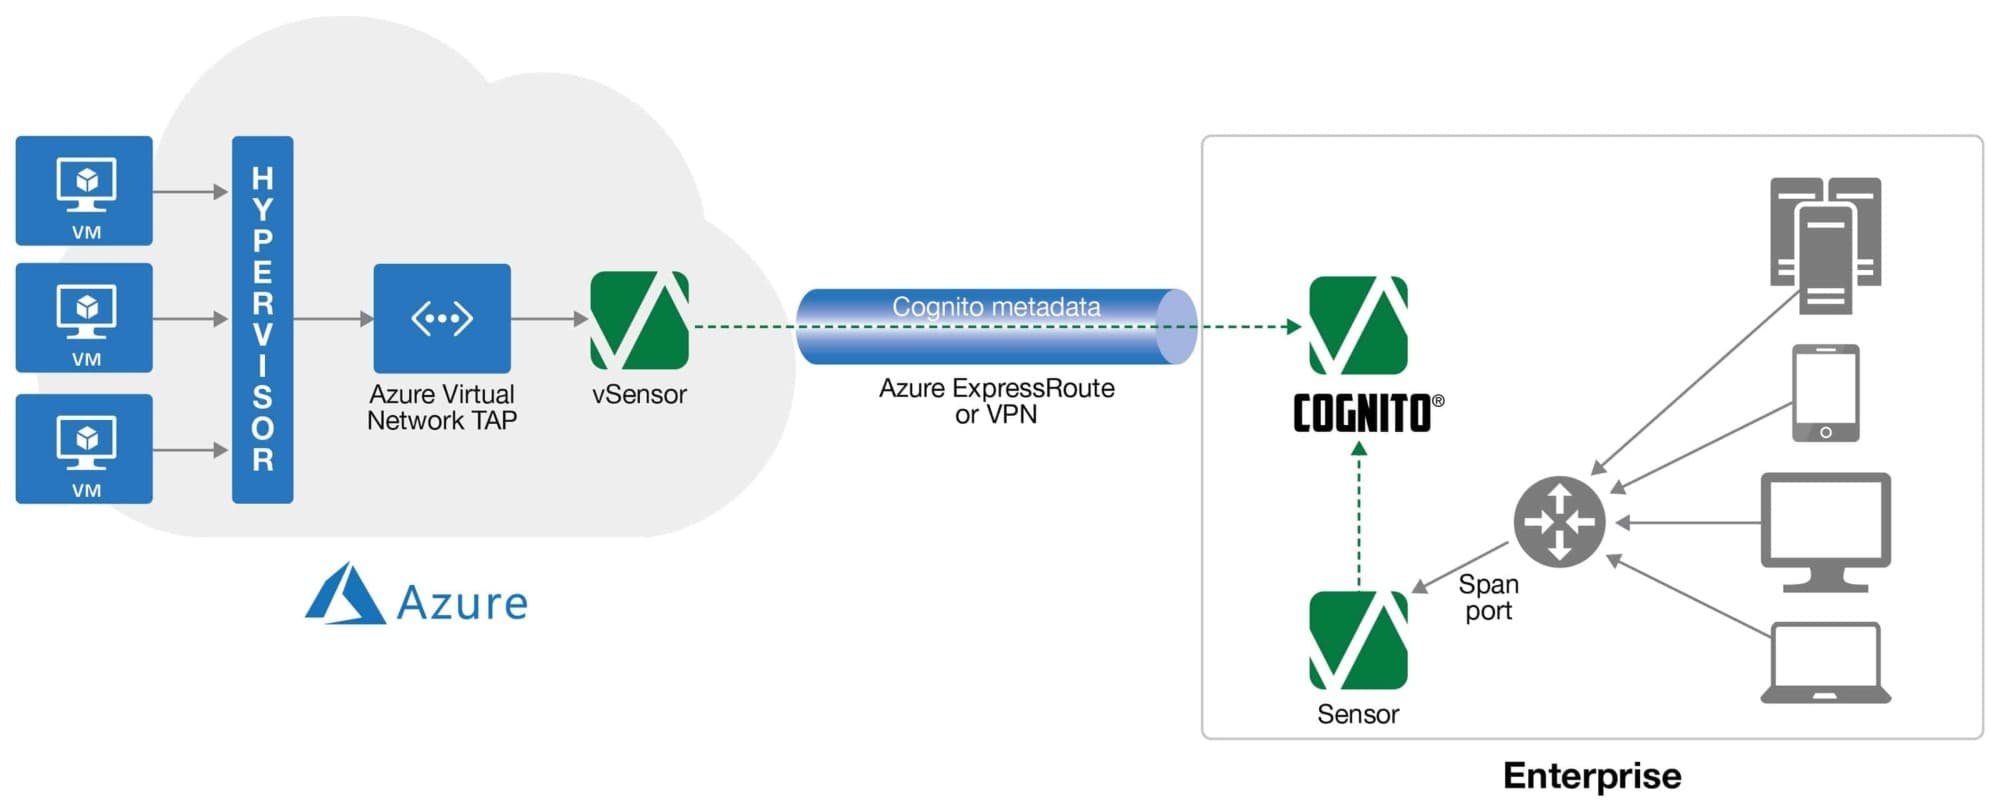
Vectra Cognito stands out in the field of threat detection by using AI-driven analytics to detect and respond to cyber threats in real-time. Its unique approach focuses on behavioral detection rather than traditional signature-based methods, allowing it to identify sophisticated attacks including insider threats. With continuous monitoring and automated response mechanisms, Vectra enhances security teams’ capabilities and reduces the time to respond to incidents. This cybersecurity solution is particularly effective for organizations seeking to simplify threat management.
Where to buy Vectra Cognito in Canada: the trusted retailers we track in this market, with the best price we have observed at each. Prices are checked regularly and can change, and the retailer confirms the final price at checkout.
We may earn a commission on purchases. It never affects our rankings.
$6,000 – $8,000
Palo Alto Networks Cortex XDR
Palo Alto Networks Cortex XDR offers a comprehensive approach to endpoint detection and response by integrating data from various sources into a unified platform. What makes Cortex stand out is its ability to correlate alerts from multiple security layers, providing enhanced visibility and detection capabilities. This holistic view enables security teams to identify and respond to threats more efficiently, minimizing potential damage. With its focus on automation and simplicity, Cortex empowers organizations to fortify their security posture.

Where to buy Palo Alto Networks Cortex XDR in Canada: the trusted retailers we track in this market, with the best price we have observed at each. Prices are checked regularly and can change, and the retailer confirms the final price at checkout.
We may earn a commission on purchases. It never affects our rankings.
$7,000 – $9,000
CrowdStrike Falcon Insight
CrowdStrike Falcon Insight is a leading endpoint protection solution recognized for its rapid incident response capabilities. Utilizing a cloud-native architecture and machine learning technology, Falcon Insight excels in providing real-time threat intelligence and prevention. Its ability to analyze vast amounts of data to detect and respond to threats effectively sets it apart from competitors. With a focus on both proactive and reactive measures, CrowdStrike is an ideal choice for organizations aiming to enhance their cybersecurity resilience.

Their innovative approach to threat detection means they can uncover advanced persistent threats that signature-based systems might miss, providing robust security.
Understanding Anomaly-Based Intrusion Detection Systems
Anomaly-Based IDS stand out for their proactive nature in identifying potential security threats. Here's what you need to know about how they work and their benefits:
1. Cutting-edge technology leverages machine learning algorithms to recognize normal baseline behavior, facilitating quick detection of anomalies.
2. Enhanced threat detection capabilities enable organizations to identify zero-day exploits—threats that have not been previously documented.
3. Data-driven insights provide cybersecurity teams with actionable information that aids in responding to potential breaches in real-time.
4. Continuous monitoring ensures that businesses can adapt to the evolving landscape of cyber threats, maintaining robust security measures.
5. Tailored alerts empower organizations to evaluate risks custom-fit to their operational needs, reducing false positives often associated with traditional systems.
6. Compliance benefits are significant, as industries are subject to regulations that mandate stringent cybersecurity measures, making anomaly-based IDS a wise investment.
Frequently Asked Questions
Which anomaly-based IDS should I pick for real-time response?
Choose Darktrace Immune System: it uses machine learning for threat detection, provides real-time monitoring and threat response, and has automated self-learning capabilities; it also has an average rating of 4.7.
What exact capability does Cisco Stealthwatch provide for anomaly detection?
Cisco Stealthwatch’s key capability is advanced network traffic analysis for threat behavior analytics, with an average rating of 4.5.
Is Darktrace Immune System worth it versus Cisco Stealthwatch?
You’d compare value using pricing, but no prices are provided for Darktrace Immune System or Cisco Stealthwatch; Darktrace has a 4.7 average rating, Cisco has 4.5.
Does Vectra Cognito focus on signatures or anomalous behavior?
Vectra Cognito focuses on detecting anomalous behavior, using AI-powered threat hunting plus real-time alerts and investigation tools; it has an average rating of 4.4.
Conclusion
In summary, Anomaly-Based Intrusion Detection Systems are crucial for safeguarding against modern cyber threats in Canada. We hope you found the information you were looking for and invite you to explore our search bar for more specific queries.